feat: synchronize immutable curated plugin releases - #3644
feat: synchronize immutable curated plugin releases#3644Patrick-Erichsen wants to merge 1 commit into
Conversation


|
🦞👀 Pull request received. I will update this pull request when review starts. ClawSweeper review completeClawSweeper finished reviewing this revision. The review result is being finalized. |

|
The latest updates on your projects. Learn more about Vercel for GitHub.
|


|
Codex review: blocked before merge. Reviewed September 9, 2026, 8:33 AM ET / 12:33 UTC (Revision 3). ClawSweeper reviewWhat this changesAdds scheduled synchronization of curated plugins into immutable releases, reviewed company-package replacements, historical download preservation, publication visibility checks, and operator reports. Regression provenancePossible regression — suspected (reviewed change). No predecessor PR is attributed. Merge readiness⛔ Blocked before merge - 6 items remain This remains useful work absent from current main. Both previously reported blockers remain on the unchanged head; the attached runtime evidence supports the feature but does not resolve those findings. Priority: P2 Review scores
Verification
How this fits togetherClawHub imports reviewed plugin sources through its existing publication and security-check pipeline. Synchronization compares source hashes, publishes changed artifacts, and directs catalog visitors to the canonical package while preserving historical releases. flowchart TD
A[Reviewed source manifest] --> B[Fetch and validate sources]
B --> C[Compare hashes and release state]
C --> D[Skip or report operator decision]
C --> E[Publish through security checks]
E --> F[Immutable release]
F --> G[Canonical catalog and redirects]
F --> H[Historical downloads and audits]
Before merge
Findings
Agent review detailsSecurityNeeds attention: Historical audit redirects can associate a security verdict with the wrong artifact; no additional authorization or supply-chain regression was established. Review metrics
Merge-risk optionsMaintainer options:
Technical reviewBest possible solution: Keep immutable publication and transactional replacement, while preserving package/version identity throughout historical audits and retaining failure reports before any publication attempt. Do we have a high-confidence way to reproduce the issue? Yes, source establishes both patch defects: open a version-pinned audit after replacing its package, or fail a fetch for a configured registry before inventory preparation. These paths were traced without executing target code. Is this the best way to solve the issue? The architecture is appropriate: it reuses the existing publisher rather than creating a parallel release store. It remains incomplete at the audit consumer and failure-report boundary; fixing those callers is narrower than removing canonical redirects or weakening inventory validation. Full review comments:
Overall correctness: patch is incorrect AGENTS.md: found and applied where relevant. Codex review notes: model internal, reasoning medium; reviewed against 6b25e866fb91. LabelsLabel changes:
Label justifications:
EvidenceSecurity concerns:
What I checked:
Likely related people:
Rank-up movesOptional improvements that raise the rating; they are not merge blockers.
Rating scale
Overall follows the weaker of proof and patch quality. Workflow
HistoryReview history (2 earlier review cycles)
|

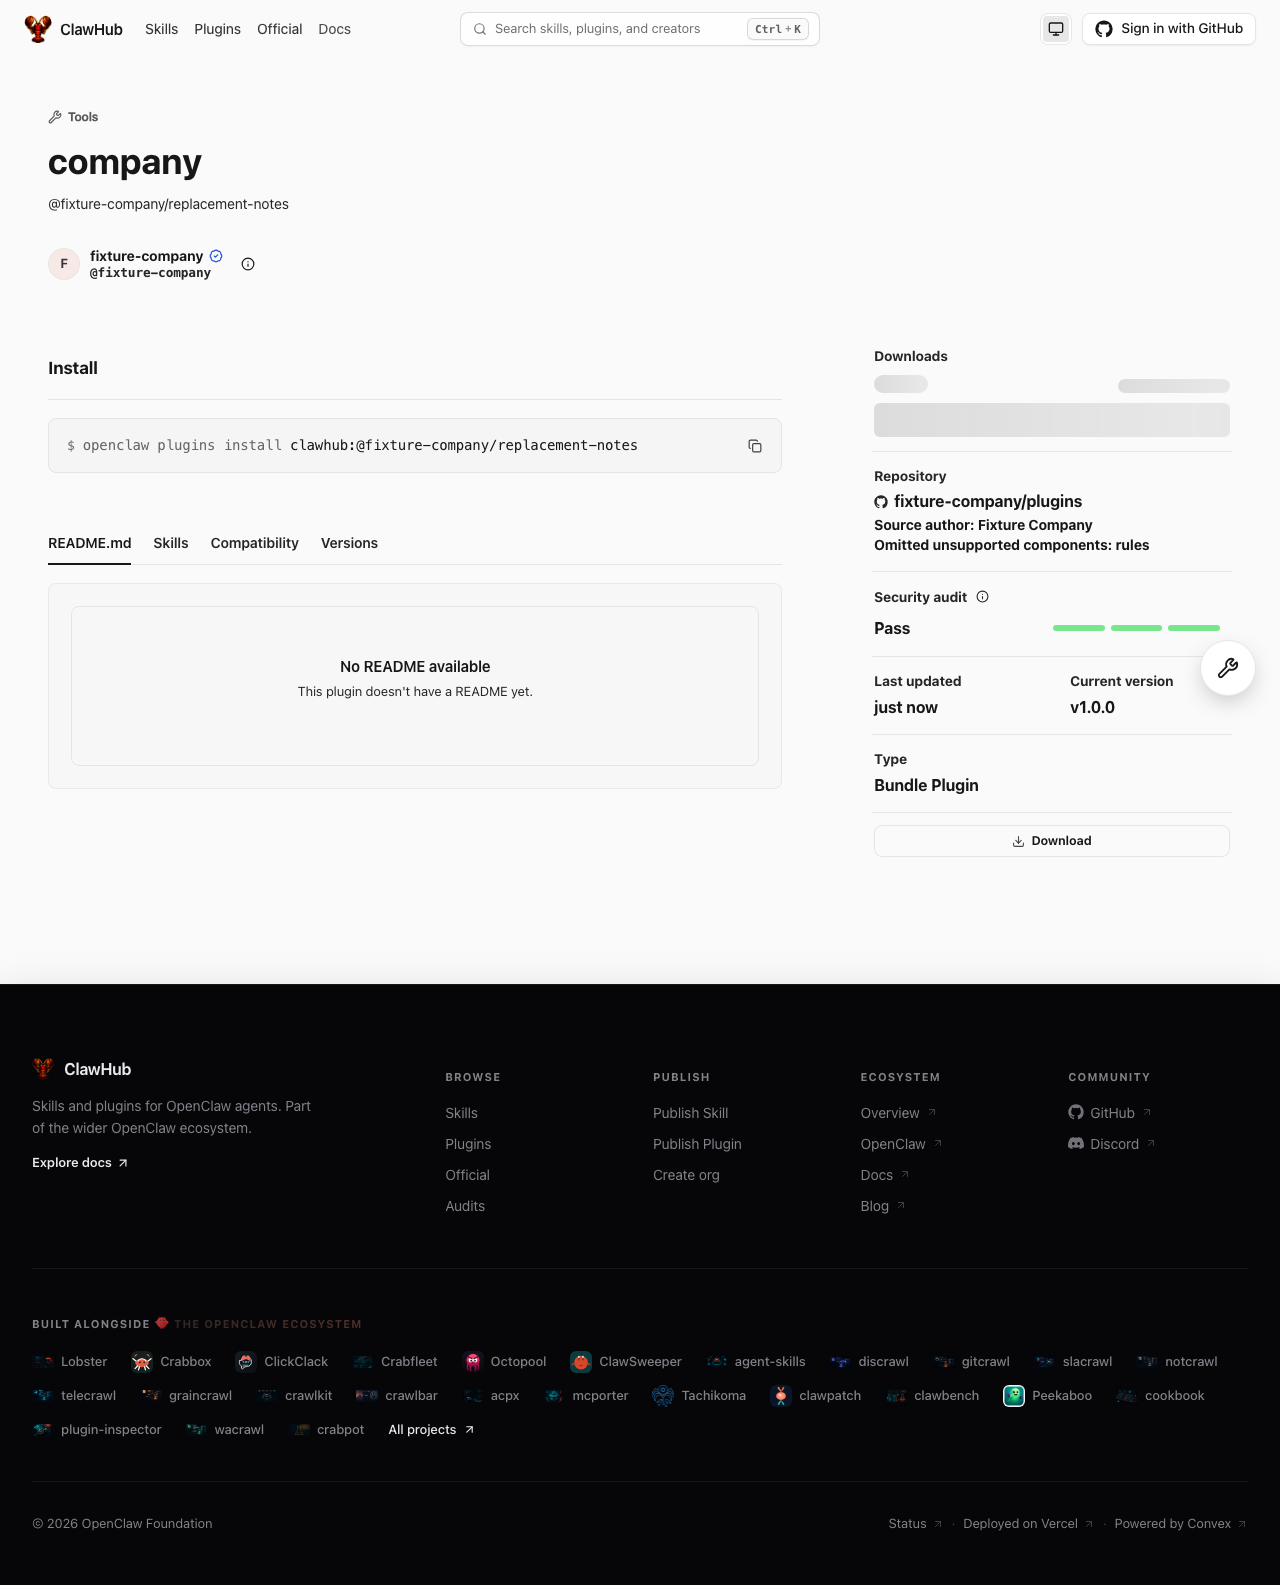
ClawHub UI ProofStatus: Canonical company package after immutable update and redirect
Raw proof files: https://github.com/openclaw/clawhub/tree/qa-artifacts/clawhub-ui-proof/pr-3644/immutable-company-plugin-sync |

ad61c85 to
5979ee9
Compare
 clawsweeper
Bot
added
P2
1 participant

Curated sources now synchronize into immutable releases: unchanged hashes are skipped, changed bytes repeat source validation and normal security checks, and reused upstream versions receive a source-hash suffix. Missing sources, identity changes, pending scans, historical rollbacks and adopted company publishers produce explicit operator decisions without overwriting the last safe release.
A reviewed company replacement publishes and redirects its registry predecessor in one transaction. Public discovery shows one canonical result; old version downloads retain their original bytes. Exact download and file routes now reject pending and blocked updates, closing a gap exposed by the real update acceptance test.
The scheduled workflow is disabled by default and runs only approved source identities on main in the Production environment. Initial bytes must match the reviewed hash; activation requires the staff token and explicit repository opt-in. The operator README covers planning, digest-bound application, custody, replacement and reporting.
Validation includes required static, coverage, type/build, package and HTTP gates, focused immutable/replacement regressions, and the real local ClawHub → archive download → OpenClaw 2026.9.3 acceptance flow. Controlled worker verdicts exercise pending, clean and malicious outcomes; they are not live ClawScan provider certification.
Final local gates: 6,547 unit tests, 17 public browser smoke checks, and the 2.5-minute catalog/download/update/replacement/OpenClaw acceptance run pass. Review findings were adjudicated against the approved scheduling contract and actual runtime proof; accepted findings are fixed. The final empty-list schema alignment and strict published-target guard were manually reviewed and covered through real Convex publication/replacement regressions.