Skip to content

feat: preserve company plugin custody and provenance - #3642

Open
Patrick-Erichsen wants to merge 1 commit into
codex/claw-723-plugin-importfrom
codex/claw-723-plugin-provenance
Open

feat: preserve company plugin custody and provenance#3642
Patrick-Erichsen wants to merge 1 commit into
codex/claw-723-plugin-importfrom
codex/claw-723-plugin-provenance

Conversation

@Patrick-Erichsen

@Patrick-Erichsen Patrick-Erichsen commented Sep 9, 2026

Copy link
Copy Markdown
Collaborator

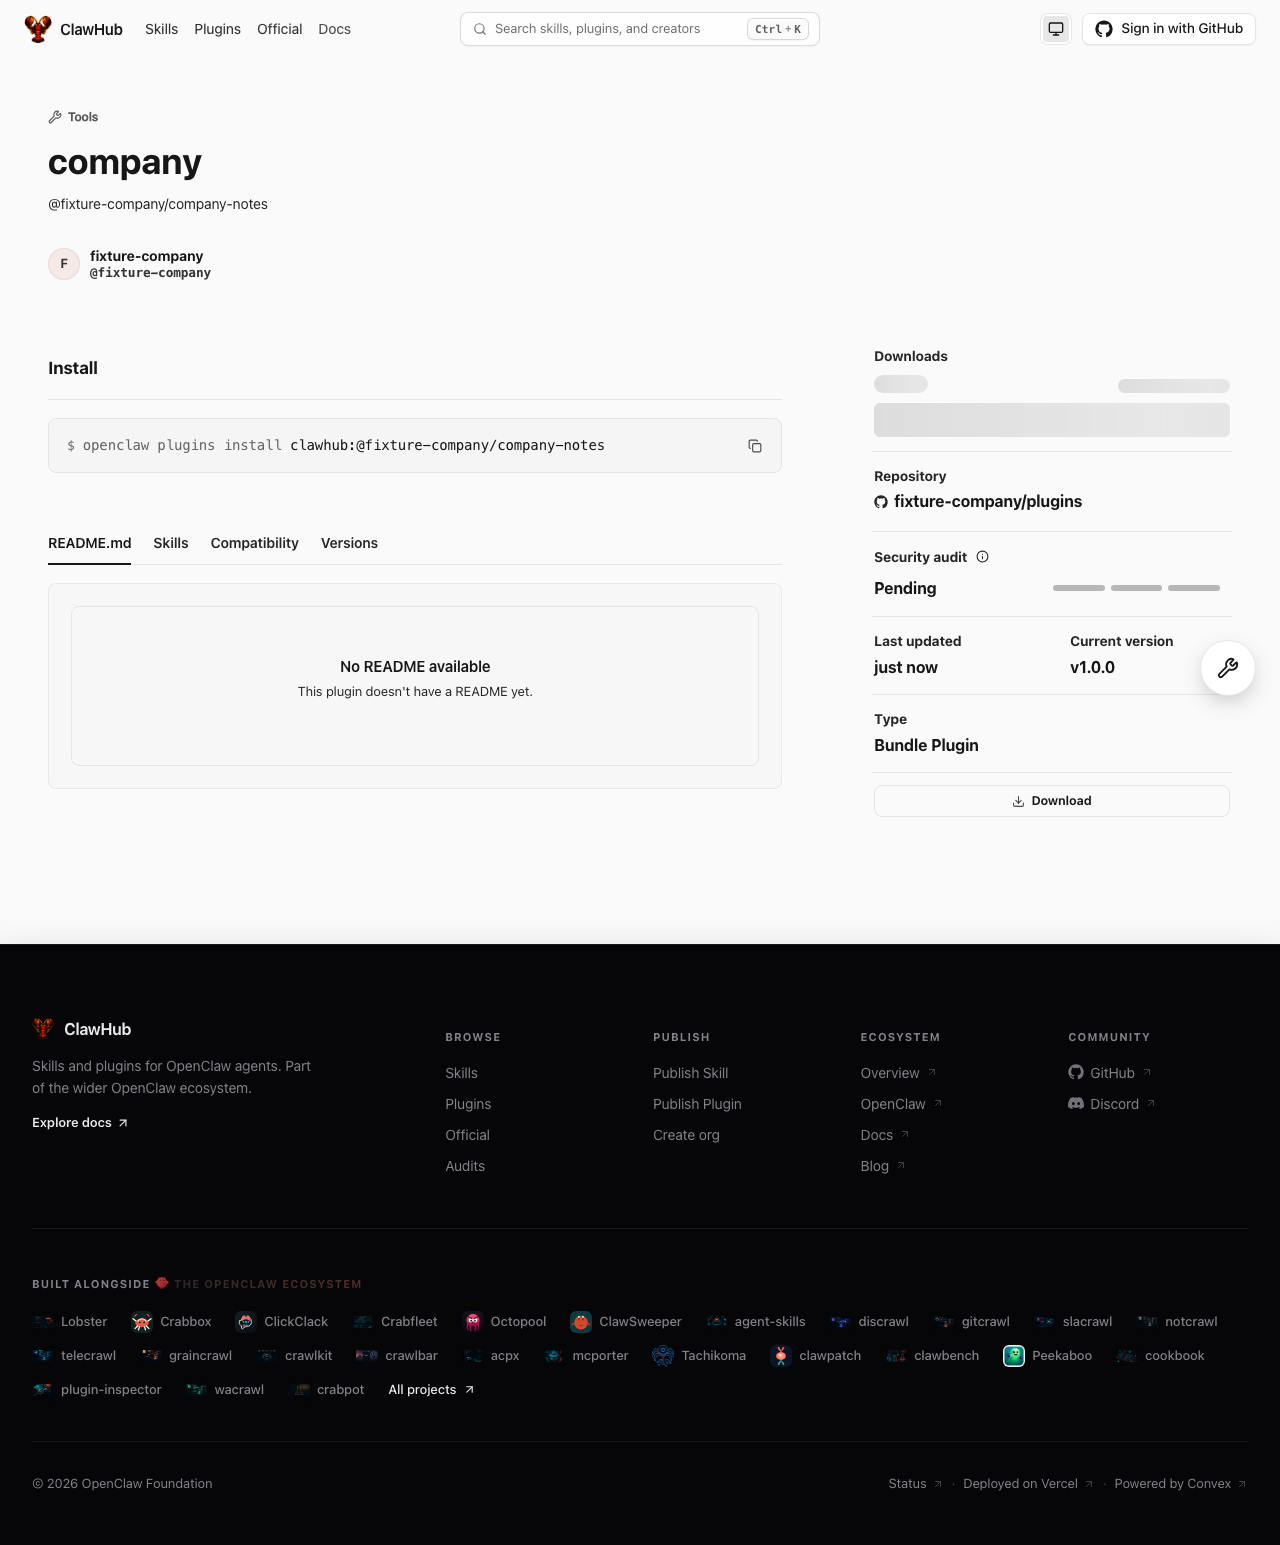
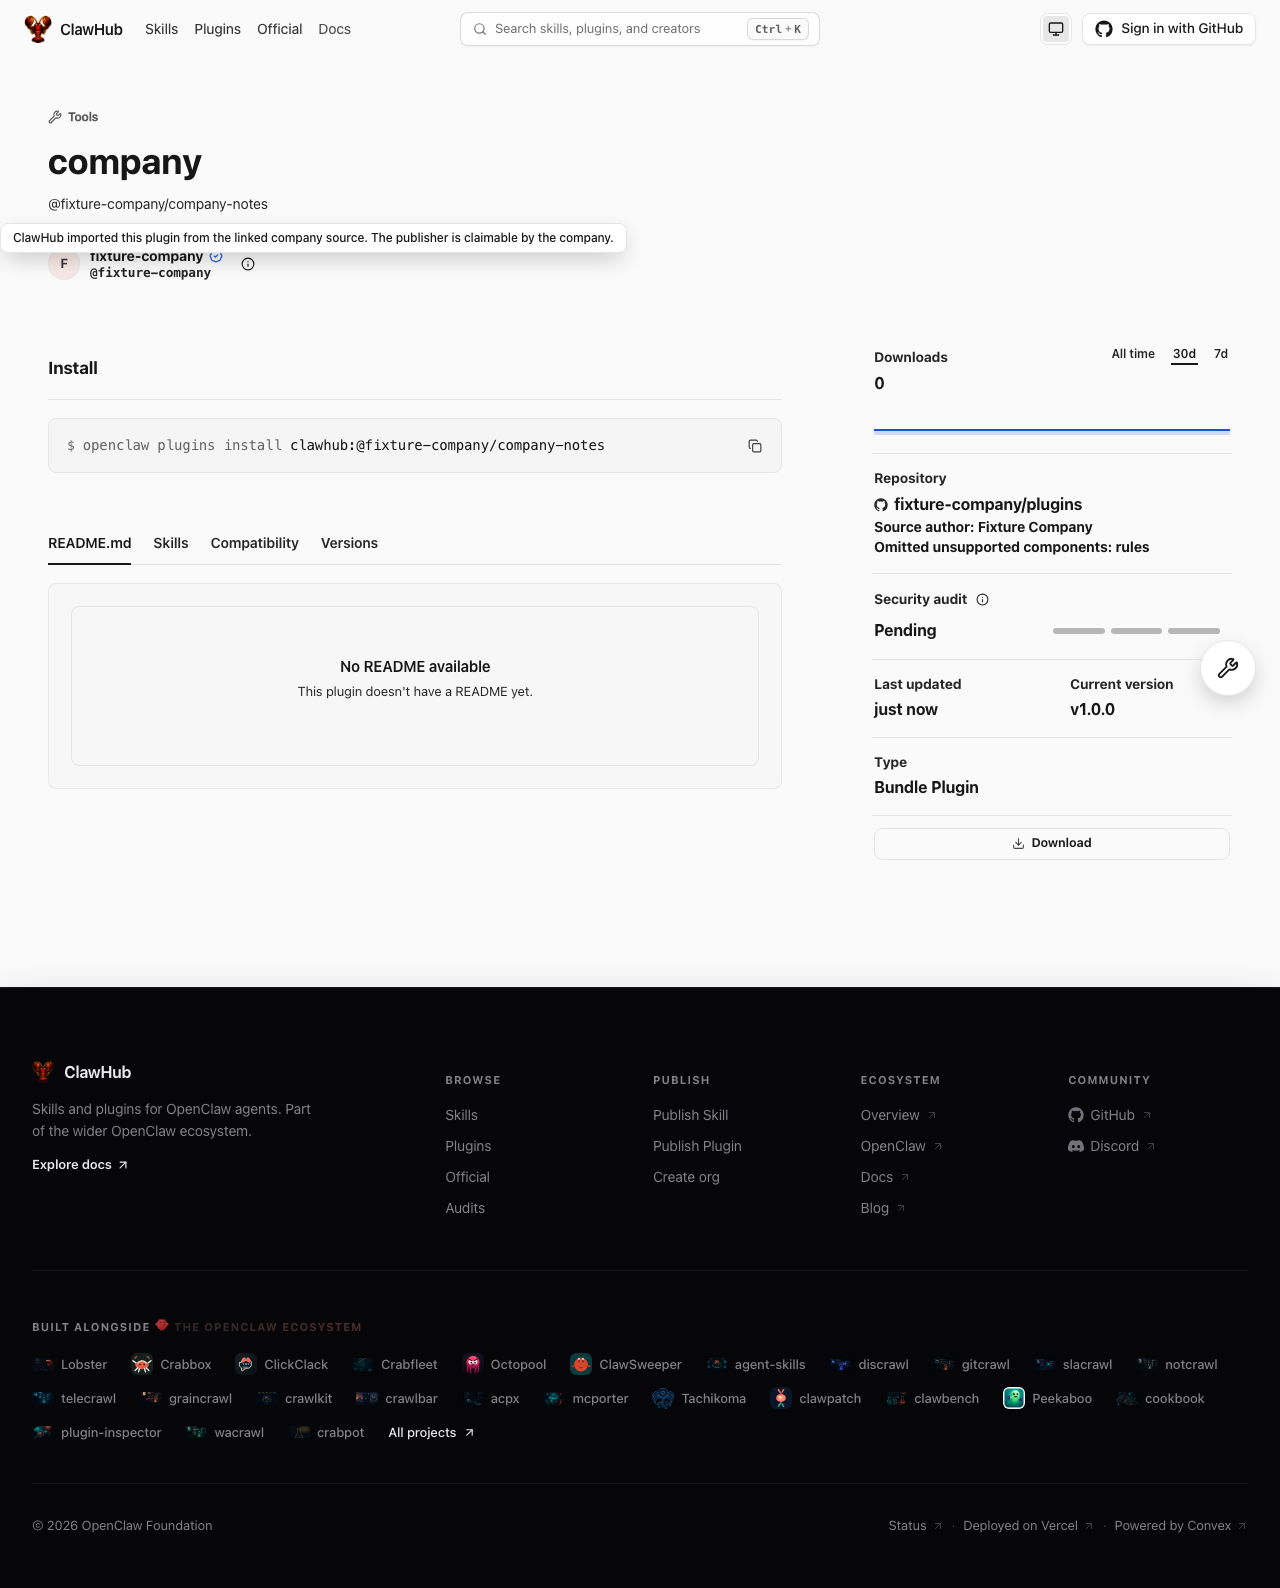
Company-owned imports now carry staff-validated provenance under a claimable organization publisher. Registry-authored bundles keep their registry namespace. The package page displays the original author, omitted components and a small custody disclosure only for a matching company-authored release; licensed source icons resolve to the exact upstream commit.

Custody requires an active staff-owned organization and the exact reviewed repository. Publication and scan completion recheck that evidence. A matching verified GitHub organization owner can adopt the publisher through the existing profile workflow while package identity and release history remain intact. Official status continues to use the existing publisher policy.

Validation: ci:static, ci:unit (6,539 tests), ci:types-build, ci:packages, ci:e2e-http, targeted custody/adoption/publication tests, and real local-auth browser proof. The local ClawHub fixture exercises company and registry publication, catalog/API provenance, the rendered custody tooltip, exact archive downloads and direct OpenClaw 2026.9.3 installs in a disposable OCM environment. Scanner verdicts are controlled worker fixtures, not live-provider certification. Autoreview is clean; the final compiler-caught lookup adjustment uses the existing version verification field and was manually checked against the API response.

Comparable before/after browser screenshots and API/install evidence were captured from the actual local ClawHub fixture.

@clawsweeper

clawsweeper Bot commented Sep 9, 2026

Copy link
Copy Markdown
Contributor

🦞👀
ClawSweeper picked this up.

Pull request received. I will update this pull request when review starts.

ClawSweeper review complete

ClawSweeper finished reviewing this revision. The review result is being finalized.

View the workflow run.

@vercel

vercel Bot commented Sep 9, 2026

Copy link
Copy Markdown
Contributor

The latest updates on your projects. Learn more about Vercel for GitHub.

Project Deployment Actions Updated
clawhub Building Building Preview Sep 9, 2026 4:06am UTC

Request Review

@clawsweeper

clawsweeper Bot commented Sep 9, 2026

Copy link
Copy Markdown
Contributor

Codex review: needs real behavior proof before merge. Reviewed September 9, 2026, 12:11 AM ET / 04:11 UTC (Revision 3).

ClawSweeper review

What this changes

Adds staff-held custody and company adoption for imported plugin publishers, preserves release provenance, and displays source attribution and custody information.

Merge readiness

Blocked before merge - 6 items remain

This remains distinct, useful work absent from current main. The previously reported publication-authorization defect remains unresolved; the supplied browser proof demonstrates the disclosure but does not settle the pending-release authority boundary.

Priority: P2
Reviewed head: 0a9a9ba612f7398cbb1b1d2610ec8162d0f9f705

Review scores

Measure Result What it means
Overall readiness 🦪 silver shellfish (2/6) Useful implementation and genuine browser evidence remain limited by an unresolved authorization defect and missing final-effect proof.
Proof confidence 🦪 silver shellfish (2/6) Needs stronger real behavior proof before merge: Authority-chain proof required: the inspected local Convex/Chromium artifacts show the disclosure and successful company/registry publication, but do not demonstrate rejection after membership revocation or custody adoption between staging and promotion through the worker and public-download boundary. This scoped requirement applies despite the collaborator exemption from unrelated proof. After adding proof, update the PR body; ClawSweeper should re-review automatically. If it does not, the PR author or someone with repository write access can comment @clawsweeper re-review.
Patch quality 🦐 gold shrimp (3/6) Security review found an item that needs attention.

Verification

Check Result Evidence
Real behavior Needs proof Needs stronger real behavior proof before merge: Authority-chain proof required: the inspected local Convex/Chromium artifacts show the disclosure and successful company/registry publication, but do not demonstrate rejection after membership revocation or custody adoption between staging and promotion through the worker and public-download boundary. This scoped requirement applies despite the collaborator exemption from unrelated proof. After adding proof, update the PR body; ClawSweeper should re-review automatically. If it does not, the PR author or someone with repository write access can comment @clawsweeper re-review.
Evidence reviewed 9 items Pinned patch and applicable policy: Reviewed the introduced af8f803..0a9a9ba changes. Read the full root AGENTS.md; no applicable nested AGENTS.md or maintainer-notes directory was found. Applied ClawHub maintainer, Convex, and retention guidance. The checkout remained clean; no builds, tests, or bundled review helpers were executed.
Publication guard still omits current membership: The introduced promotion guard reloads the actor and publisher but calls a validator that checks only actor role, publisher kind, source identity, and custody. It does not query publisherMembers or reject deleted/deactivated actors and publishers. By contrast, insertReleaseInternal checks active state and current organization publish membership before staging. The finalization action and its claim mutation do not supply the missing membership check.
Existing reusable authorization boundary: getPublisherMembership and requirePublisherRole already provide indexed current-membership and active-publisher checks. Reusing these at promotion is narrower than introducing another authorization policy. The new provenance validator deliberately receives only role/kind/handle/custody fields, so it cannot enforce active state itself.
Findings 1 actionable finding [P1] Recheck publisher membership before promoting curated releases
Security Needs attention Revoked publisher access survives until publication: The promotion transaction validates stored provenance and staff role without checking current organization membership, allowing a previously authorized actor's queued release to become public after access removal.

How this fits together

ClawHub imports plugin artifacts into organization publishers and holds releases pending security checks. Custody and publisher authorization determine whether those releases can become publicly discoverable and downloadable.

flowchart TD
  A[Reviewed company source] --> B[Staff import]
  B --> C[Pending plugin release]
  D[Publisher membership and custody] --> B
  C --> E[Security checks]
  E --> F[Publication authorization]
  D --> F
  F --> G[Public catalog and downloads]
  H[Verified company adoption] --> D
Loading

Before merge

  • Add real behavior proof - Needs stronger real behavior proof before merge: Authority-chain proof required: the inspected local Convex/Chromium artifacts show the disclosure and successful company/registry publication, but do not demonstrate rejection after membership revocation or custody adoption between staging and promotion through the worker and public-download boundary. This scoped requirement applies despite the collaborator exemption from unrelated proof. After adding proof, update the PR body; ClawSweeper should re-review automatically. If it does not, the PR author or someone with repository write access can comment @clawsweeper re-review.
  • Recheck publisher membership before promoting curated releases (P1) - The prior blocker remains. If a staff actor stages a curated release and an organization owner removes their publisher membership before scans finish, this guard still passes: validateCuratedPluginPublisher checks the admin role and custody, but never current membership. Promotion then marks the release published. Recheck current organization publish access and active actor/publisher state in this transaction, as admission already does, while preserving the explicit manual-recovery path.
  • Resolve security concern: Revoked publisher access survives until publication - The promotion transaction validates stored provenance and staff role without checking current organization membership, allowing a previously authorized actor's queued release to become public after access removal.
  • Resolve merge risk (P1) - The supplied runtime evidence does not establish rejection after publisher membership is revoked or custody is adopted while a release awaits scans.
  • Resolve merge risk (P1) - The schema additions are optional, but the prior request for upgrade evidence preserving existing publishers, releases, and downloads remains unaddressed.
  • Complete next step (P2) - Repair the promotion authorization guard and supply the authority and upgrade evidence listed above. Redact credentials, private endpoints, and personal information. Update the PR body to trigger re-review; if it does not run, ask a maintainer to comment @clawsweeper re-review.

Findings

  • [P1] Recheck publisher membership before promoting curated releases — convex/packages.ts:11447-11455
  • [high] Revoked publisher access survives until publication — convex/packages.ts:11447
Agent review details

Security

Needs attention: The new custody authorization check permits queued publication after organization publish access is revoked.

Review metrics

Metric Value Why it matters
Change size +798/-80 across 23 files The change spans backend authorization, persistent metadata, API schemas, import tooling, and UI.
Production and test LOC Production +413/-19; tests +309/-60; generated +66/-1; specs +10 Production growth supports the stated custody and provenance feature, with separate regression and browser coverage.

Merge-risk options

Maintainer options:

  1. Revalidate authority at promotion (recommended)
    Use current membership and active-state checks in the publishing transaction, then demonstrate that revocation and adoption prevent queued releases from becoming downloadable.

Technical review

Best possible solution:

Reuse current publisher authorization atomically at release promotion, preserving the audited recovery exception and proving existing records retain their identities and download behavior.

Do we have a high-confidence way to reproduce the issue?

Yes, for the remaining patch defect: stage a curated release, remove the staff actor's publisher membership while retaining their admin role, then complete clean scans. Source shows promotion does not recheck membership; this sequence was not executed during the read-only review.

Is this the best way to solve the issue?

Not yet. Extending existing organization profiles and release metadata is appropriate, but authorization must be enforced in the final publication transaction; admission-only validation cannot cover changes while scans run.

Full review comments:

  • [P1] Recheck publisher membership before promoting curated releases — convex/packages.ts:11447-11455
    The prior blocker remains. If a staff actor stages a curated release and an organization owner removes their publisher membership before scans finish, this guard still passes: validateCuratedPluginPublisher checks the admin role and custody, but never current membership. Promotion then marks the release published. Recheck current organization publish access and active actor/publisher state in this transaction, as admission already does, while preserving the explicit manual-recovery path.
    Confidence: 0.99

Overall correctness: patch is incorrect
Overall confidence: 0.97

AGENTS.md: found and applied where relevant.

Codex review notes: model internal, reasoning medium; reviewed against 39ff7db30c2e.

Labels

Label justifications:

  • P2: This is a bounded new publisher-custody feature rather than an established production outage.
  • merge-risk: 🚨 security-boundary: Queued curated releases can pass the new promotion guard after organization publish membership is revoked.
  • rating: 🦪 silver shellfish: Overall readiness is 🦪 silver shellfish; proof is 🦪 silver shellfish and patch quality is 🦐 gold shrimp.
  • status: 📣 needs proof: The PR needs real behavior proof before ClawSweeper can clear the contributor ask. Needs stronger real behavior proof before merge: Authority-chain proof required: the inspected local Convex/Chromium artifacts show the disclosure and successful company/registry publication, but do not demonstrate rejection after membership revocation or custody adoption between staging and promotion through the worker and public-download boundary. This scoped requirement applies despite the collaborator exemption from unrelated proof. After adding proof, update the PR body; ClawSweeper should re-review automatically. If it does not, the PR author or someone with repository write access can comment @clawsweeper re-review.

Evidence

Security concerns:

  • [high] Revoked publisher access survives until publication — convex/packages.ts:11447
    The promotion transaction validates stored provenance and staff role without checking current organization membership, allowing a previously authorized actor's queued release to become public after access removal.
    Confidence: 0.99

What I checked:

  • Pinned patch and applicable policy: Reviewed the introduced af8f803..0a9a9ba changes. Read the full root AGENTS.md; no applicable nested AGENTS.md or maintainer-notes directory was found. Applied ClawHub maintainer, Convex, and retention guidance. The checkout remained clean; no builds, tests, or bundled review helpers were executed. (AGENTS.md:1, 0a9a9ba612f7)
  • Publication guard still omits current membership: The introduced promotion guard reloads the actor and publisher but calls a validator that checks only actor role, publisher kind, source identity, and custody. It does not query publisherMembers or reject deleted/deactivated actors and publishers. By contrast, insertReleaseInternal checks active state and current organization publish membership before staging. The finalization action and its claim mutation do not supply the missing membership check. (convex/packages.ts:11447, 0a9a9ba612f7)
  • Existing reusable authorization boundary: getPublisherMembership and requirePublisherRole already provide indexed current-membership and active-publisher checks. Reusing these at promotion is narrower than introducing another authorization policy. The new provenance validator deliberately receives only role/kind/handle/custody fields, so it cannot enforce active state itself. (convex/lib/publishers.ts:503, 0a9a9ba612f7)
  • Re-review continuity: The prior review identified the same missing finalization check. Local comparison against b7d6356 failed because required historical objects were unavailable; reading that exact revision through the GitHub contents API confirmed the same promotion guard. This is a repeated blocker, not a newly discovered late finding. (convex/packages.ts:11447, 0a9a9ba612f7)
  • Real browser and publication evidence: Inspected both downloaded screenshots and the linked report/summary from feat: preserve company plugin custody and provenance #3642 (comment). They identify baseline f969a2d and candidate b7d6356, local Convex/dev-auth, Chromium, and controlled security-worker fixtures. The candidate visibly shows the custody tooltip, source author, and omitted components at the reported local fixture URL. Catalog output shows successful company and registry publication; the report also states OpenClaw 2026.9.3 installation validation. Report blob identity: 9e07998f7a1de85fb0fafa46646233e6bf7dcf49. These artifacts do not exercise membership revocation or adoption between staging and promotion. (clawhub-ui-proof/pr-3642/company-plugin-custody/report.md, 39ff7db30c2e)
  • Authority and upgrade coverage: The new runtime tests cover staff-only custody establishment, repository matching, adoption authorization, and initial pending visibility. The real local-auth scenario covers clean and malicious scanner outcomes, API provenance, downloads, and disclosure. It does not revoke publisher access during pending publication or exercise pre-existing records without the new fields through an upgrade. (e2e/local-auth/company-plugin-sync.pw.test.ts:134, 0a9a9ba612f7)

Likely related people:

  • unknown: The claimed source-line change could not be verified from bounded local history. (role: source history unknown; confidence: low)
  • steipete: Suggested for follow-up; no historical authorship or introduction is verified. (role: unverified routing candidate; confidence: low)

Rank-up moves

Optional improvements that raise the rating; they are not merge blockers.

  • Recheck current organization publish membership and active actor/publisher state atomically before curated-release promotion.
  • Provide redacted runtime traces showing authorized publication succeeds while membership revocation and company adoption prevent pending releases from becoming downloadable.
  • Demonstrate that existing publishers and releases without the new fields preserve identities, visibility, and download behavior after upgrade.

Rating scale

Score Internal tier Crab rank Meaning
6/6 S 🦀 challenger crab Exceptional readiness
5/6 A 🦞 diamond lobster Very strong readiness
4/6 B 🐚 platinum hermit Good normal PR; ordinary maintainer review
3/6 C 🦐 gold shrimp Useful, but confidence is limited
2/6 D 🦪 silver shellfish Proof or implementation needs work
1/6 F 🧂 unranked krab Not merge-ready
N/A NA 🌊 off-meta tidepool Rating does not apply

Overall follows the weaker of proof and patch quality.
Shiny media proof means a screenshot, video, or linked artifact directly shows the changed behavior. Runtime, network, CSP, and security claims still need visible diagnostics.

Workflow

  • ClawSweeper keeps one durable marker-backed review comment per issue or PR.
  • Re-runs edit this comment so the latest verdict, findings, and automation markers stay together instead of adding duplicate bot comments.
  • A fresh review can be triggered by eligible @clawsweeper re-review comments, exact-item GitHub events, scheduled/background review runs, or manual workflow dispatch.
  • PR/issue authors and users with repository write access can comment @clawsweeper re-review or @clawsweeper re-run on an open PR or issue to request a fresh review only.
  • Maintainers can also comment @clawsweeper review to request a fresh review only.
  • Fresh-review commands do not start repair, autofix, rebase, CI repair, or automerge.
  • Maintainer-only repair and merge flows require explicit commands such as @clawsweeper autofix, @clawsweeper automerge, @clawsweeper fix ci, or @clawsweeper address review.
  • Maintainers can comment @clawsweeper explain to ask for more context, or @clawsweeper stop to stop active automation.

History

Review history (2 earlier review cycles)
  • reviewed 2026-09-09T03:05:55.382Z sha b7d6356 :: needs real behavior proof before merge. :: [P1] Recheck publisher membership before promoting curated releases
  • reviewed 2026-09-09T03:33:42.230Z sha b7d6356 :: needs real behavior proof before merge. :: [P1] Recheck publisher membership before promoting curated releases

@Patrick-Erichsen

Copy link
Copy Markdown
Collaborator Author

ClawHub UI Proof

Status: passed
Mode: before-after
Scenario: company-plugin-custody
Provider: local Convex/dev-auth; real Playwright Chromium; controlled security-worker fixtures
Baseline: f969a2d082
Candidate: b7d6356b09

Company package before custody disclosure Company package with custody and provenance disclosure

Raw proof files: https://github.com/openclaw/clawhub/tree/qa-artifacts/clawhub-ui-proof/pr-3642/company-plugin-custody

@clawsweeper clawsweeper Bot added P2 Normal backlog priority with limited blast radius. merge-risk: 🚨 security-boundary 🚨 Merging this PR could weaken sandboxing, authorization, credentials, or sensitive data. rating: 🦪 silver shellfish Thin PR readiness signal; proof, validation, or implementation needs work. status: 📣 needs proof The PR needs real behavior proof before ClawSweeper can clear the contributor ask. labels Sep 9, 2026
Sign up for free to join this conversation on GitHub. Already have an account? Sign in to comment

Labels

merge-risk: 🚨 security-boundary 🚨 Merging this PR could weaken sandboxing, authorization, credentials, or sensitive data. P2 Normal backlog priority with limited blast radius. rating: 🦪 silver shellfish Thin PR readiness signal; proof, validation, or implementation needs work. status: 📣 needs proof The PR needs real behavior proof before ClawSweeper can clear the contributor ask.

Projects

None yet

Development

Successfully merging this pull request may close these issues.

1 participant